The Breakdown of Traditional Domain Boundaries
The entire model of consumer privacy protection rested on a clean architectural line. Code served directly from the site you chose to visit counted as first-party content, treated as safe. Code pulled in from an outside marketing domain counted as third-party tracking, and basic content filters could flag and block it on sight. That distinction was simple enough for a blocklist to enforce, which is exactly why it worked for so long.
CNAME cloaking erases that line. By manipulating the configuration records that sit underneath the Domain Name System, trackers now present themselves as ordinary subdomains of the website you already trust. The filter looks at the address, sees a name belonging to the host site, and waves the script through. The blocklist never fires because, on paper, there's nothing on the list to match.
How Tracker Masking Deceives Browser Security
The trick happens at the network routing layer—before any content reaches your device. And the consequence matters: because your browser reads the tracking code as a native part of the site, it hands that code the elevated privileges reserved for first-party scripts.
Here's how the disguise is assembled:
- The architectural alias. A site owner sets up a DNS alias called a CNAME record. That record points an innocent-looking subdomain—something like
tracker.trustedwebsite.com—straight at an external data broker's server. The name says “trustedwebsite.” The destination says something else entirely. - The first-party illusion. When you load the page, your security client inspects the subdomain address and sees only the local, trusted name. It files the incoming script under first-party code rather than flagging it as an invasive third-party utility. The misclassification is the whole point.
- The unrestricted harvest. Now operating with first-party privileges, the cloaked script gets the kind of access third-party trackers are normally denied. It can read secure authentication cookies, capture detailed behavioral inputs, and stream telemetry back to the broker's network—all under cover of a connection your browser believes is local.
Because the tracking endpoint is structurally indistinguishable from the main site, perimeter defenses and simple blacklists register nothing out of place. The surveillance runs inside the trusted data stream itself, opening an invisible pipeline for profiling you never agreed to.
“Trackers exploit fundamental DNS trust boundaries to bypass browser privacy filters, accessing secure authentication cookies and telemetry under a trusted name.”
Canonical name redirection transforms invasive third-party tracking scripts into privileged native actors.
Technical Strategies for Deep Packet Resolution
Defeating masked tracking means abandoning surface-level domain matching in favor of resolving where the data actually goes. CNAME cloaking is built specifically to obscure that destination, so any defense that trusts the visible URL is defending an entrance the attacker already walked past.
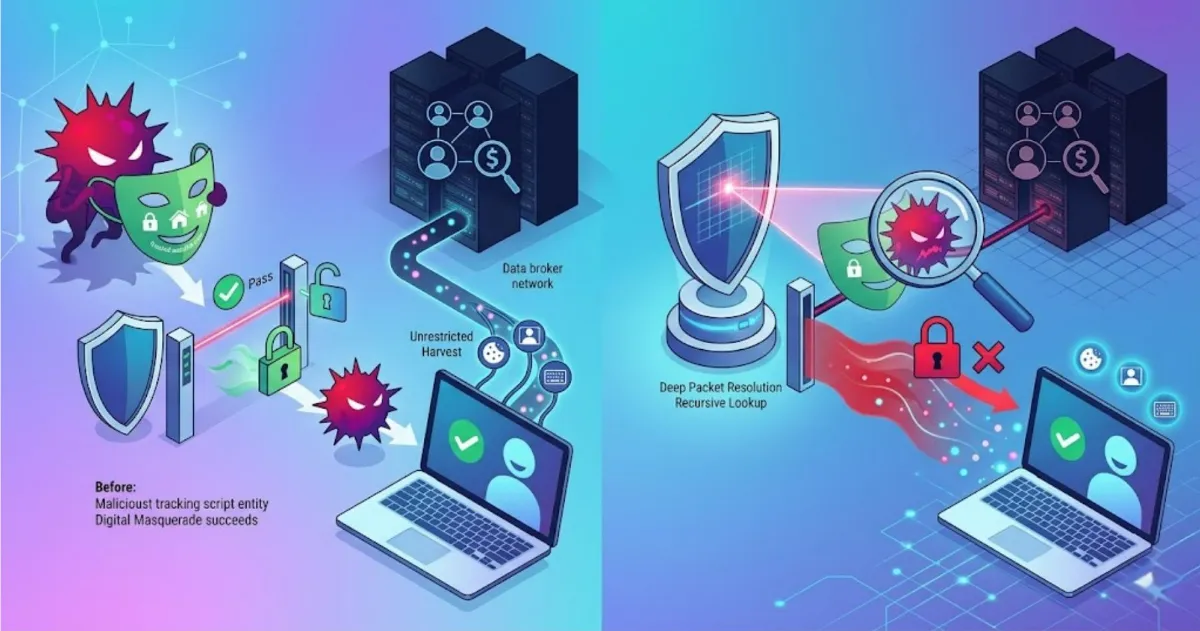
The sound approach is real-time canonical name resolution carried out inside the browser environment. Rather than accepting the first-party alias at face value, the security utility runs a recursive lookup on every outbound request—peeling back the friendly subdomain to expose the real IP address and the parent domain hosting the script. Once the browser is forced to evaluate the ultimate endpoint instead of the cosmetic mask, the broker hiding behind the trusted infrastructure becomes visible, and the tracking sequence can be intercepted before any data leaves your machine.
Put plainly: don't ask what the connection calls itself. Follow the chain until you find what it resolves to, then decide.
Securing Your Web Sessions with the Total Adblock Browser Extension
For anyone who would rather not perform recursive DNS lookups by hand, the Total Adblock browser extension automates the work of catching disguised scripts that lean on CNAME cloaking. Tracker masking borrows your browser's native trust architecture, but the underlying data still has to reach an unverified external surveillance network—and that outbound leg is where it gets caught. The extension analyzes structural web code, performs advanced script inspection, and severs connections to known data brokers and invasive advertising platforms no matter how the destination is dressed up.
The result is a faster, cleaner, more orderly browsing experience. If you spend time streaming, it also removes in-play video ads so playback runs without interruption.
The extension stays out of your way, running in the background without demanding complex technical setup. Total Adblock offers tailored filtering through intuitive presets, letting you manage executable elements around what matters most to you—whether that's advanced privacy or stricter system security. You keep full authority over your own list of trusted websites and acceptable connections. By putting this extension to work, you stop external servers from exploiting deceptive domain architecture to compromise your digital identity.